

Protocol Analysis WCNA Exam Dumps [2024] Practice Valid Exam Dumps Question
WCNA Dumps - Grab Out For [NEW-2024] Protocol Analysis Exam
The Wireshark Certified Network Analyst (WCNA) certification is a popular and highly-valued credential in the field of network analysis. Wireshark Certified Network Analyst Practice Exam certification is offered by the Wireshark University, which is a leading provider of training and resources related to network analysis and troubleshooting. The WCNA certification is designed to validate an individual's knowledge and skills in using Wireshark, a powerful network protocol analyzer, for network troubleshooting and analysis.
Passing the Protocol Analysis WCNA certification exam demonstrates the candidate's proficiency in network analysis and troubleshooting, making them a valuable asset to any organization. It also provides a competitive edge in the job market, as employers look for certified professionals who can quickly identify and resolve network issues. Overall, the Protocol Analysis WCNA certification is an excellent investment for anyone looking to advance their career in network analysis and gain recognition for their expertise in the field.
NEW QUESTION # 55
Wireshark's Export feature can be used to identify HTTP objects and reassemble them into their original format.
- A. False
- B. True
Answer: B
NEW QUESTION # 56
Both the capture and display filter syntax for ARP requests and replies is arp.
- A. False
- B. True
Answer: B
NEW QUESTION # 57
DHCP is based on BOOTP.
- A. False
- B. True
Answer: B
NEW QUESTION # 58
The TCP Time-Sequence graph can depict packet loss.
- A. False
- B. True
Answer: B
NEW QUESTION # 59 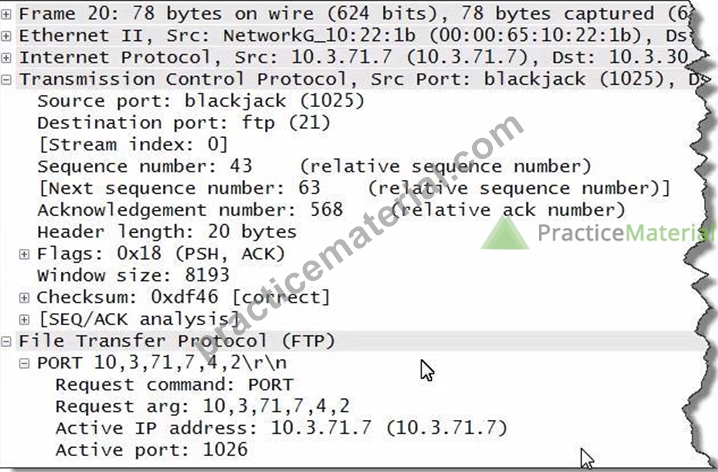
Which statement about this packet is correct?
- A. The sender will open port 1026 for an FTP data connection.
- B. This communication is generated by the "Blackjack" application.
- C. The receive window size value indicates no additional data can be received on port 1025.
- D. The packet is a request to the target to open port 1026 for a new TCP connection.
Answer: A
NEW QUESTION # 60
All packets that contain UDP or TCP headers are counted in the IP Protocol Types statistic.
- A. False
- B. True
Answer: B
NEW QUESTION # 61
The capture and displayfilter syntax for TCP communications is tcp.
- A. False
- B. True
Answer: B
NEW QUESTION # 62
Which statement about TCP sequence and acknowledgment numbering is correct?
- A. Starting Sequence Numbers cannot be larger than 65,535 because this is a 2-byte field.
- B. The sequence number always increments by 1 for each data packettransmitted.
- C. The Acknowledgment Number field indicates the next sequence number expected from the other side of the connection.
- D. Both sides of a TCP connection must agree on an Initial Sequence Number value.
Answer: C
NEW QUESTION # 63 
This packet shows the expanded TCP flags area. The display filter tcp.fiags.syn==1 && tcp.flags.ack==1 and the display filter tcp.fiags=0xi2 provide identicalfiltering results.
- A. False
- B. True
Answer: B
NEW QUESTION # 64
You may need to capture traffic at different points on the network to identify the location of packet loss.
- A. False
- B. True
Answer: B
NEW QUESTION # 65
With a few exceptions, display filters use the same syntax as capture filters.
- A. True
- B. False
Answer: B
NEW QUESTION # 66
How do you determine which Profile is in use while you are capturing traffic?
- A. Lookin the Status Bar Profile column.
- B. Right-click on the Packet Summary pane.
- C. Examine the Wireshark Title Bar.
- D. Open the Preferences | Interface information.
Answer: A
NEW QUESTION # 67
What is the purpose of creating Wireshark profiles?
- A. create a customized method of name resolution
- B. customize Wireshark for more efficient analysis in specific environments
- C. create a manageable database of packets for use in third-party programs
- D. discover and test RSA keys for traffic decryption
Answer: B
NEW QUESTION # 68 
Which statement about this Wireshark image is correct?
- A. This is a live capture process.
- B. This trace file is part of a trace file set.
- C. A display filter has been applied to this traffic.
- D. These packets have been saved to a trace file already.
Answer: A
NEW QUESTION # 69 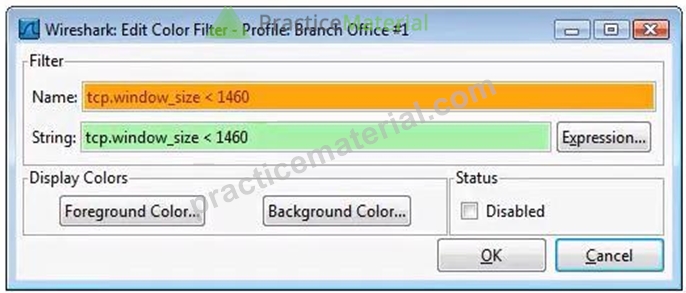
Which statement aboutthis color rule is correct?
- A. This color rule will generate a syntax error.
- B. This color rule must be placed under all other TCP color filters.
- C. This color rule will be saved in the Branch Office #1 profile.
- D. This color rule is based on the BerkeleyPacket Filter (BPF) format.
Answer: C
NEW QUESTION # 70
By default, Mergecap combinestrace files based on the order they are listed on the command-line.
- A. True
- B. False
Answer: B
NEW QUESTION # 71
1O Graphs supportdisplay filters and expressions.
- A. False
- B. True
Answer: B
NEW QUESTION # 72
TCP data is sequenced and acknowledged to ensure delivery.
- A. False
- B. True
Answer: B
NEW QUESTION # 73
Null scans use legal TCP packet formats, but listen for illegally-formed TCP response packets.
- A. True
- B. False
Answer: B
NEW QUESTION # 74 
Which statement about this packet is correct?
- A. The source and destination hosts support window scaling.
- B. This packet is establishing window scaling between the two TCP hosts.
- C. The Window Size field value indicates that no additional data can be received by 10.0.52.164.
- D. The Sequence Number field value is too low to allow additional data segments to be received by10.0.52.164.
Answer: A
NEW QUESTION # 75
How do you quickly spot large gapsin time between packets in a trace file containing 6,000 packets?
- A. Set the Time column toSeconds Since Previously Displayed Packetand sort the Time column.
- B. Open and examine Wireshark'sExpert Infoswindow.
- C. Set the Time column toSeconds Since Beginning of Captureand scroll through the trace file.
- D. Look for packets colorized based on Wireshark's default coloring rule for high delta times.
Answer: A
NEW QUESTION # 76
The capture filterport 67 would capture all DHCP traffic seen by Wireshark.
- A. True
- B. False
Answer: B
NEW QUESTION # 77
When you apply a display filter, the Status Bar indicates the total number ofpackets captured and the packets displayed.
- A. False
- B. True
Answer: B
NEW QUESTION # 78
DNS responses contain four sections: Question, Answer RR, Authority RR and Additional RR.
- A. False
- B. True
Answer: B
NEW QUESTION # 79
If a DHCP client does not receive an acknowledgment before the expiration of the rebinding time, the DHCP client must release its IP address and send a DHCP broadcast tolocate a DHCP server or Relay Agent.
- A. False
- B. True
Answer: B
NEW QUESTION # 80
......
WCNA Exam Dumps PDF Guaranteed Success with Accurate & Updated Questions: https://testking.practicematerial.com/WCNA-questions-answers.html
